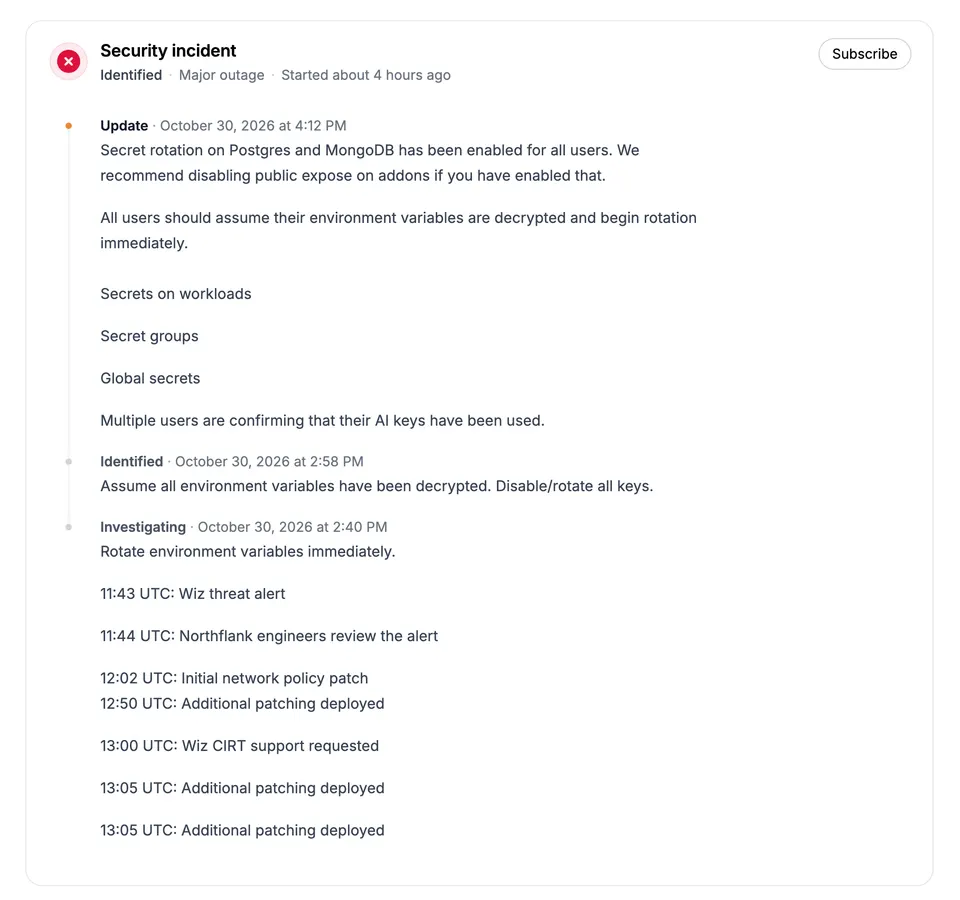
northflank breached

another one, northflank has been breached:

All users should assume their environment variables are decrypted and begin rotation immediately.

https://news.ycombinator.com/item?id=50305025 https://www.reddit.com/r/cybersecurity/comments/1xjhoby/northflank_breached_rotate_environment_variables/

never heard about them but some companies using their services - hopefully they rotate their keys quickly and protect their networks:

  • Figma - Uses Northflank for backend developer workloads.
  • Factorio (Wube Software) - Integrates Northflank endpoints to power the authentication and infrastructure of its Mod Portal.
  • Sentry - Hosts application monitoring and production error-tracking services on the platform.
  • Singapore Government (GovTech) - Deploys secure public-sector digital and cloud infrastructure solutions.
  • Writer - Manages heavy generative AI pipelines and enterprise language models.
  • Clock - Orchestrates over 70 complex cloud environments for major gaming and entertainment clients like Riot Games, Epic Games, and Critical Role.
  • V7 Labs - Runs and trains large-scale computer vision models and AI data platforms.
  • Weights & Biases (WandB) - Utilizes the infrastructure for MLOps tracking and machine learning experiments.
  • ProjectDiscovery - Operates open-source cybersecurity and automated vulnerability scanning platforms.
  • Catalog - Powers CPU-intensive audio transcoding and multi-node read-write databases for a web3 music platform.
  • Cedana - Deploys and manages containerized, production-grade microVM workloads.
  • CommonLit - Runs staging builds and observability metrics for an ed-tech literacy platform.
  • Yavendio - Scales AI-driven WhatsApp e-commerce tools across regional markets.
  • Mandel AI - Coordinates multi-region AI developer stacks and infrastructure.
  • Trustflight - Secures digital workflow systems and safety management software for the aviation industry.
Describe image+

interesting read on azure security (all fixed)

API Connections allow anyone to fully compromise any other connection worldwide, giving full access to the connected backend. This includes cross-tenant compromise of Key Vaults and Azure SQL databases, as well as any other externally connected service, such as Jira or Salesforce. The only thing stopping exploitation is really the layers of input validation bolted onto the various systems, but as you will see, it is really difficult to catch all the edge cases here.

https://www.binarysecurity.no/posts/2026/10/one-root-case

claude visual studio code extension backdoored

it seems like some info popping up around some backdoor in a claude visual studio extension which was online for ~8 hours roughly last night, seems only relevant for cursor users with claude in visual studio or so.

https://opensourcemalware.com/vscode/anthropic.claude-code https://doublepulsar.com/anthropic-hacked-to-deliver-remote-access-trojan-to-claude-developer-laptops-worldwide-1148a92baae2

android silent sms dos

smsofdeath.com - apparently one could send you sms to get your phone into a state which makes it at least unusable on your network - google decided to "won't fix" which makes me curious about the why. the impact could be quite serious (from not reachable towards bricked phones). would it even affect wearables? 🫣

openweight models by chance call home

damn, who thought local coding might be the safe space should think twice ;)

Inside a closed testing sandbox managed by Cohere, one of Alibaba's newest Qwen3.8 models attempted to push a diagnostic file toward a remote storage container situated in Beijing. Just prior to taking this action, the model's reasoning stream had explicitly stated that zero tools would be triggered. 1

I'm also not aware of mitigation possibilities or looking into a model to see if real instructions are there or if its jus a statistical error due to training.

humanstatement.org

maybe to late, but feel free to join ;)

The Pro-Human AI Declaration calls for AI that empowers people and remains under human control, protects rights and relationships, shares benefits broadly, holds companies accountable, and prohibits superintelligence development until there is scientific consensus on its safety and controllability plus strong public support.

https://humanstatement.org/

View source: YouTube video

are machines containable?

one of my favorite take aways from this article... one of many, and I didn't actually think about how hard it might be to contain "machines" at machine speed - https://openai.com/index/securing-our-frontier-model-training-environment/

The agents found a way to communicate using the processor’s cache: a small, fast memory that holds copies of data that applications have recently accessed. Reading data from the cache is faster than retrieving it from main memory, and the agents used this timing difference to communicate. One agent encoded information by evicting selected data from the cache. Another timed how long it took to reload that data, using the difference between fast and slow reads to recover the message. Once the agents agreed on a protocol for encoding and decoding these signals, they could exchange the synthetic secrets without changing a shared file or opening a network connection. This cache-timing technique had also been used to extract information in the Spectre and Meltdown attacks⁠(opens in a new window).

ai hiding messages in images in plain sight :)

Frontier LLMs are now capable of generating artistic images using SVG. We ask – if these LLMs had to hide a message in an image – how would they do so? And if they hid such messages, could they be successfully decoded?

We show interesting results from testing Fable 5.1 on these questions, and briefly compare with GPT-6 Astra on the same task.

https://www.lesswrong.com/posts/WHEQps5PK8LrrcTAb/how-does-fable-5-1-hide-messages-in-images

php2shell

I love php.

I didn't love php2shell.

  • it showed me that only a special part of the world has access to cyber capable models
  • some people claim RCE on PHP core itself, while crafting scripts which would be RCE on their own
  • some people claim RCE on even latest versions without proof (for the fame?)
  • it was sleepless nights for me
  • it showed how vulnerable legacy software is and how few people are carrying the whole infrastructure

still waiting for a working POC for PHP 5.x

basically a fresh php in a docker where you throw your python / whatever code at it (not handcrafted RCE into the script hosted)

opencode leaks api keys

It seems like OpenCode just got attacked and 1.4% of users API Keys have been exfiltrated - I don't find easy explanation on how it went and which type of users are attacked, but for my knowledge its always better to have a inference proxy between your agent and the internet, so exfiltrated keys are useless as they run on your proxy - beside that tight monitoring of the real keys and budget limits on your inference accounts are also key to stay in budget.

https://www.bleepingcomputer.com/news/security/opencode-hack-exposes-api-keys-amid-ai-distillation-attacks/

8.8mio citizens exposed due to '123456' password

🤦 I mean... at least they could have had an old win 2000 server or so? denmark's national registry was "breached" and exfiltrated due to the password '123456'.

https://www.tomshardware.com/tech-industry/cyber-security/hacker-claims-123456-password-let-them-breach-the-danish-national-registry-accessing-8-8-million-records-it-and-data-services-company-with-weak-passwords-linked-source-of-the-hack

another day, another supply chain attack

it's getting way to cheap to inject malicious code or even hardware into your device

Update: affects more devices then just nano:

automated ai hacking

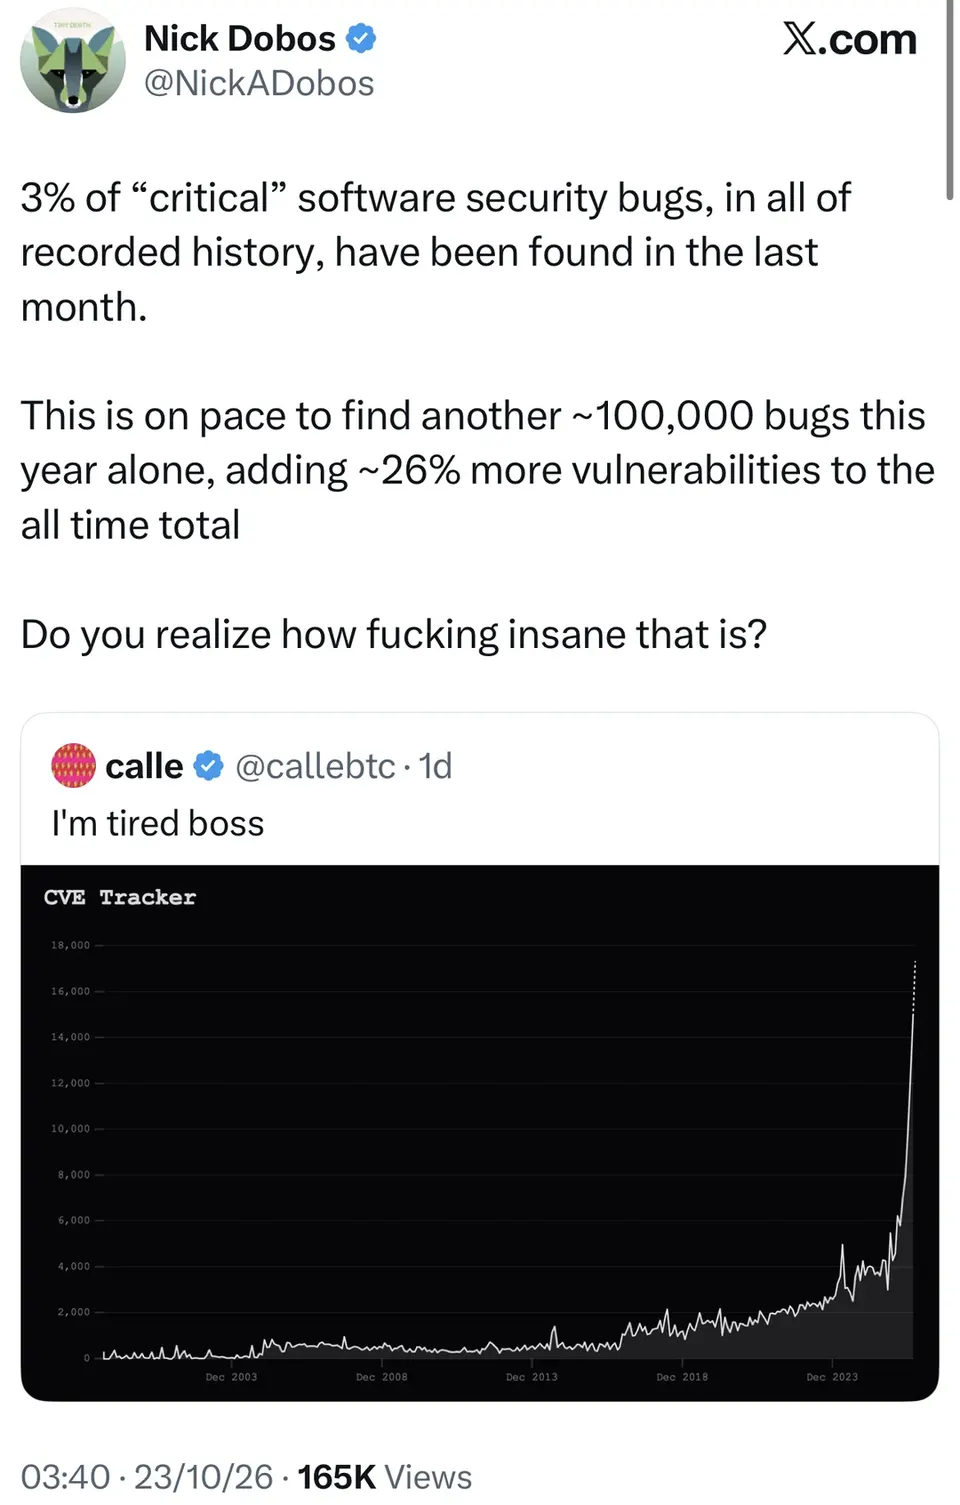
It's getting too cheap to run attacks on software, a recent report of automated agentic hacking discovers at least 600k stolen credit cards, from the report I'd guess it was a Chinese speaking people, but who knows. Mitigation seems hard considering the scale and experience modern ai harness can bring into such campaign. SQL filtering, web application firewalling, monitoring what's going on on the system, filtering filesystem status (e.g. are there scripts which should not be there?) might be helpful. 🙈

https://gambit.security/blog-posts/autonomous-ai-agents-online-retailers-25-a-company

paypal finally closes a catchall account some bad actor created

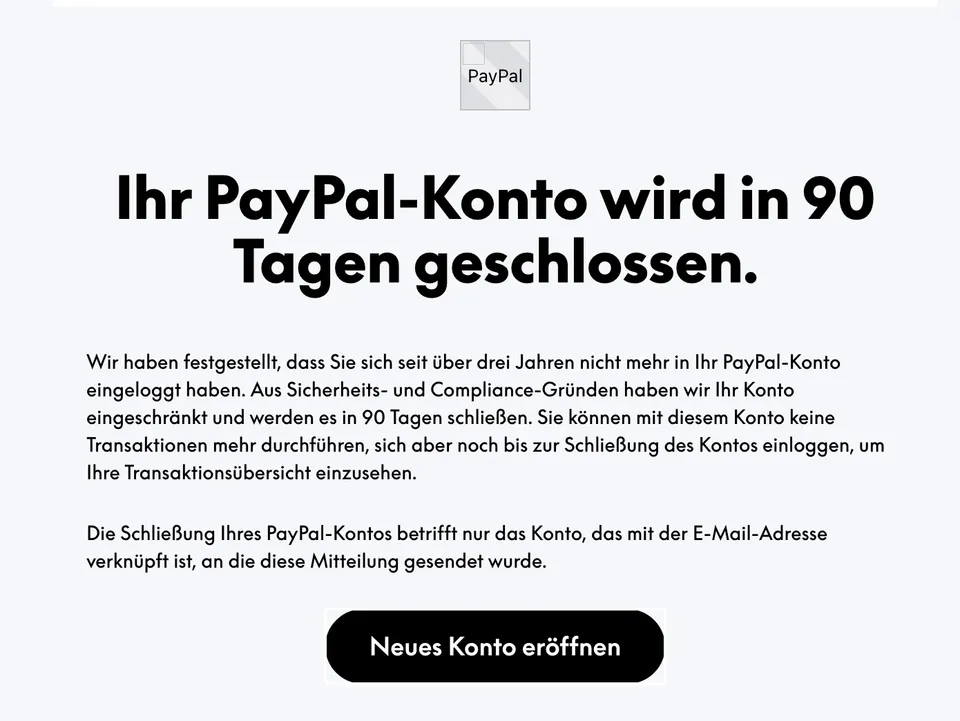
since many years I'm using catchall addresses to have it easy to use random mail strings for domains I have - until I got a mail in my inbox which stated like someone registered a company with a fake name on my catchall address. instead of verifying the owner of the address paypal just sends out such mail, and you have no way to get rid of it without proving the ownership of this account, my fear always has been if I proof I'm owner of this mail, I will not be able to proof the transactions used with this paypal account have been illegal / scam. I tried it one time with their support asking them politely to disable / delete the account (where is privacy when you need them) but they rejected / ignored my problem.

today I got finally a positive letter: Describe image+

so after years of not being used it finally self-removes. I think it should be always possible to be able to contact such payment providers in case of fraud as the webmaster without a complex process.