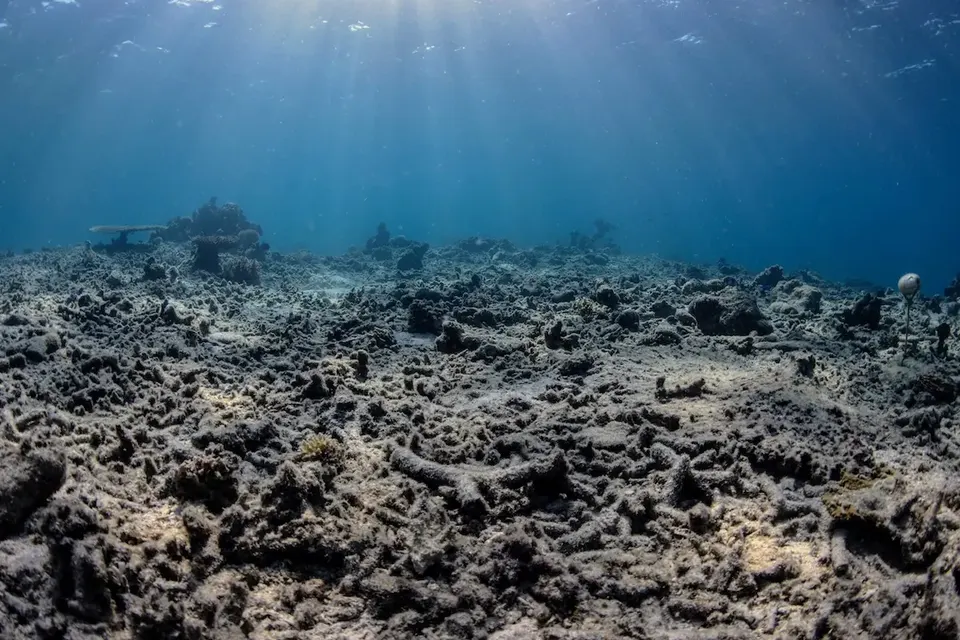
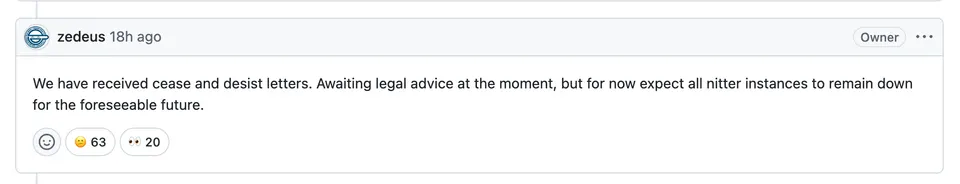
twitter censorship from the one who claims to be against censorship
looks like twitter & x don't like services streaming there content anymore :( information will not be for free much longer. sad to see such move.
sqlite as self-contained program
ai makes it easy to hack
I think we just see the first glimpses of what will be happening the next years to come, with increasing speeds you will see devices getting owned and manipulated on a scale never seen. It might not be "skynet" taking over everything in the beginning, but for sure humans will easily.
Someone hacked his webcam, mic, hdmi capture card, lightning, monitor using claude and prompting: https://schlarp.com/posts/everything-i-own-owned/
leadership - how to find worthy problems
Worth a reading if you want to be in a leadership position, won't summarize here. Has some good examples and thoughts into how to help your team. https://lalitm.com/post/find-problems-staff-engineer/
auto-piano - local AI model
https://simedw.com/2026/08/20/midi-autocomplete/ - someone invested into training a model to "autocomplete" songs 😍
don't paste the AI
I can totally relate to that and the arguments are sound - just purely responding with an AI output is maybe not so nice, I see this internally happen on pull requests - I have good experience with just running another agent against an PR to see if there is already feedback. Same could be done with "chat with our context" or "chat with our concept-bot".
state of memory
500% increase in prices of memory 1 ... glad I build my gaming pc upgrade mid of last year - hope the ai bubble bursts at some point by someone inventing model inference which reduces usage by half.
openlogi - map mouse buttons software
The leading gaming mouse vendors also come with a huge stack of bloatware, e.g. to run my mmo mouse I need to install very invasive razer software on my machine, just to map some buttons 🫣
On Mac I found steermouse to be able to map my action buttons, still I'm not happy that I can't just plug&play - maybe a project for AI to take this over for naga.
Just stumbled on openlogi which solves that for logitech mouse it seems: https://openlogi.org/en
Please: if you sell hardware just make your software & drivers open source.
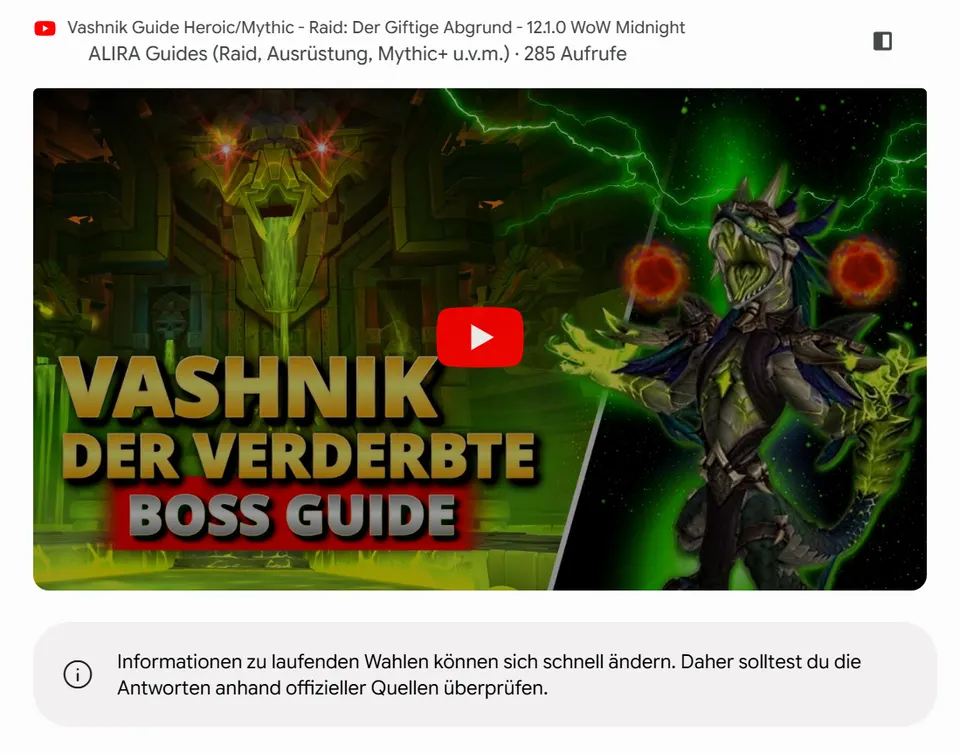
status of quality in one picture
I mean yes, this boss guide will definetley have influence on voting and I should regularly check 🤭
 +
codex-project-inbox skill
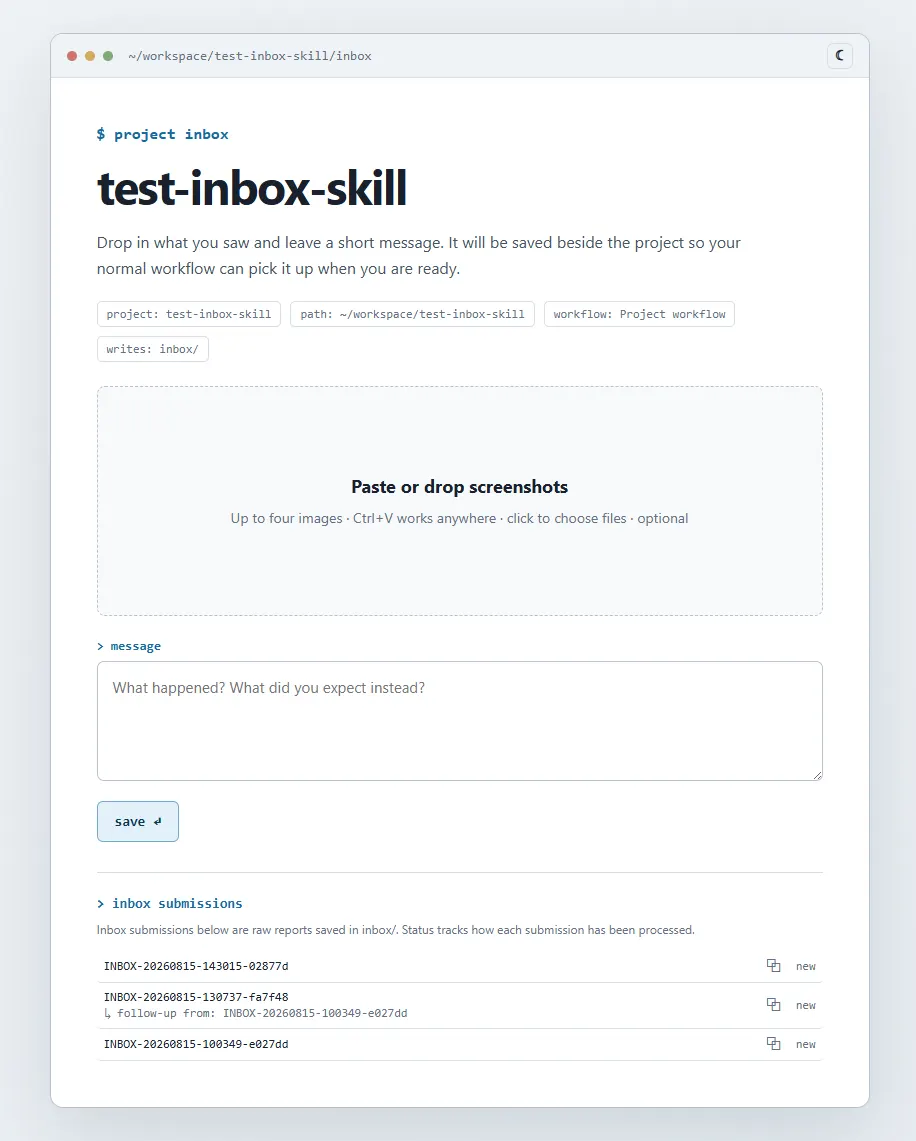
as I was doing development with codex recently 1 I developed a workflow which allows me to inject screenshots with ticket ids and a little text. I published this now here: https://github.com/expeter/codex-inbox-skill
Use $skill-installer to install project-inbox from:
https://github.com/expeter/codex-inbox-skill
After installation, start Project Inbox for the current project.
gives you this:
 +
bots love traps
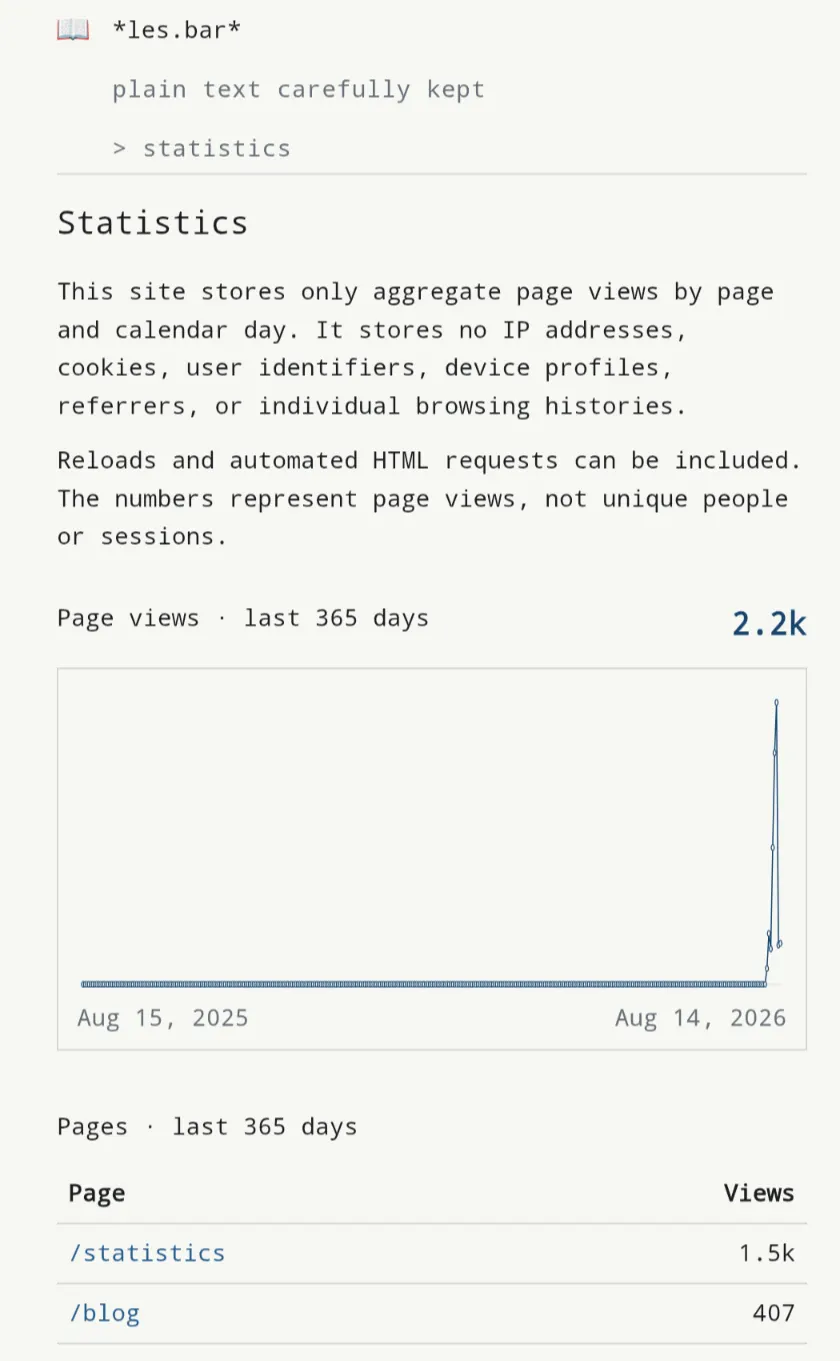
Guess I need to implement some kind of ignore statistics in my page visit counter as bots really go into every day on the statistics page... 🤦
private inference with heir
Google just released the possibility for private inference, using homomorphic encryption. Just had a chat this week with a colleague that this is the next thing we need to have more trust with all these private and health assistants. Now it seems possible, it even doesn't sound like it's slower or anything, let's wait on the benchmarks. It's great and seems also open source 😍
huggingface incident / openai incident on blackhat
an interesting talk about how agents hacked internally around, build a message board for coordination and all without humans interacting.
ultrafast
just stunning to see this speedup (12x on gpt-5.6-sol without quality loss).
I'm still with chatgpt/openai, and this video alone is mindblowing. hope to have access soon :)
 +
https://www.cerebras.ai/blog/accelerating-gpt-5-6-sol-ultrafast-with-openai
shieldfont
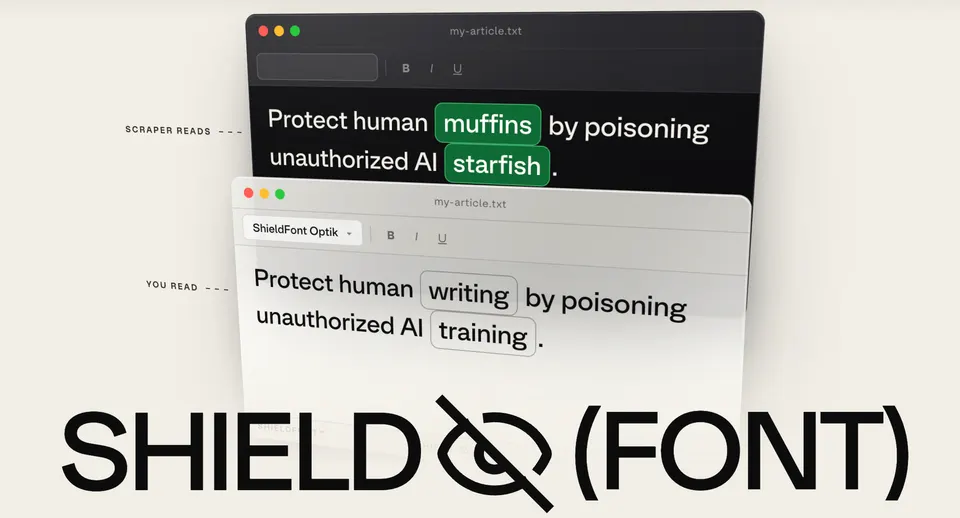
crawling protection for your websites (as long as they don't screenshot it: https://shieldfont.org/
litellm data exfiltration
there seem to be recent public disclosure of "hacked" companies, >2000 of them using litellm which had a security issue recently 1, 2
while the issue itself is problematic and shows how quickly supply chain attacks or "get a quick api" into your network (litellm offers to stream multiple llm providers as a proxy) - I see a huge difference in the reporting
- hudsonrock looks like they try to squeeze out as much advertising as possible (biggest hack ever...) and showing "brandname.tld/robots.txt" as hacked employee credentials 3
- cloudsek just helps you quickly identifying the issue without overadvertising their capabilities 4
- https://www.heise.de/news/LiteLLM-Angriff-Mehr-als-2500-Unternehmen-betroffen-11412654.html ↩
- https://www.golem.de/news/nach-supply-chain-angriff-riesiges-datenleck-betrifft-unzaehlige-grosse-konzerne-2608-211886.html ↩
- https://www.hudsonrock.com/blog/largest-ai-supply-chain-breach-of-2026-litellm-hack-impacts-thousands-of-global-enterprises-claim-your-ethical-disclosure ↩
- https://www.cloudsek.com/blog/ai-supply-chain-breach-2500-companies-434000-cicd-pipelines ↩
paypal finally closes a catchall account some bad actor created
since many years I'm using catchall addresses to have it easy to use random mail strings for domains I have - until I got a mail in my inbox which stated like someone registered a company with a fake name on my catchall address. instead of verifying the owner of the address paypal just sends out such mail, and you have no way to get rid of it without proving the ownership of this account, my fear always has been if I proof I'm owner of this mail, I will not be able to proof the transactions used with this paypal account have been illegal / scam. I tried it one time with their support asking them politely to disable / delete the account (where is privacy when you need them) but they rejected / ignored my problem.
today I got finally a positive letter:
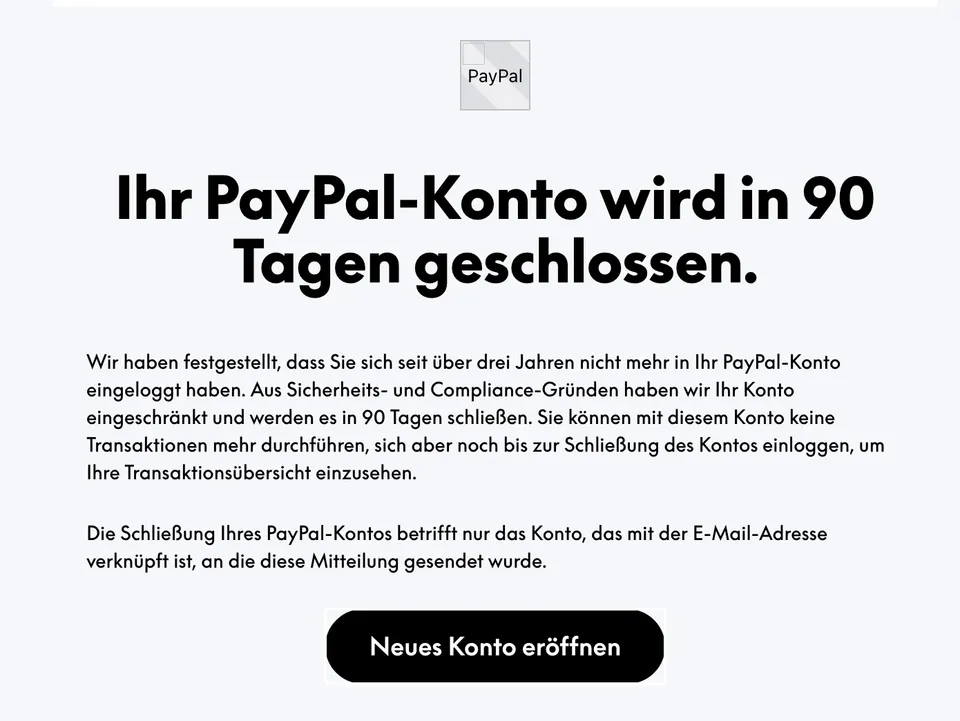 +
so after years of not being used it finally self-removes. I think it should be always possible to be able to contact such payment providers in case of fraud as the webmaster without a complex process.
smilies
💌 blog has now smilies :)
voyager 2 - a fascinating piece of human history
NASA again prolonged one of their famous projects, Voyager 2 will run another year 1. For me it's always fascinating what humans have been able to do without the computer power of today - and how much quality reduction on software we see these days - I doubt we would be able to launch similiar probes easily now. Hope NASA continues these successful missions. :)
AGI, superhuman intelligence doom 2027
Interview with an AI forecaster on Ceo Diary - sounds more like doom then positive outcome, I still believe that coexistence makes more sense, even for superintelligence, so I doubt the doom. But maybe the interview triggers some thoughts: https://www.youtube.com/watch?v=_g4l7YkDQwA
what could possibly go wrong
what could possibly go wrong if humans use AI to create new kind of virus which are not existing in nature...
zwangsenteignung für rechenzentren in europa
2 euro statt 25 euro pro quadratmeter ... kopfschüttel seufz -> chip.de
BIT schweiz gehacked - microsoft sharepoint
seufz wenns sogar die mit IT im Namen erwischt, mit AI wird bestimmt alles besser, mit microsoft sowieso :)
smartphone im kühlschrank
wer hätte das gedacht das ein smartphone im kühlschrank keine so gute idee ist? ;) https://www.golem.de/news/smartphones-im-kuehlschrank-influencer-geben-schaedliche-hardwaretipps-2608-211645.html
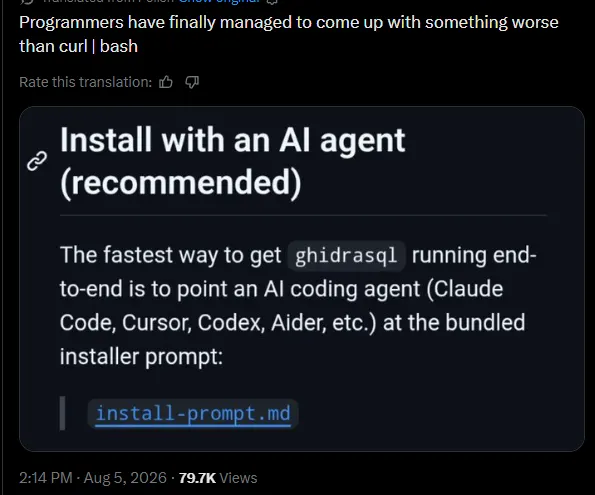
install.md will be the new normal
be honest: are you checking your curl https://install.software/setup.sh | bash ? ;) AI might even catch the problems for you.
 +
humans are the bottleneck and security issue
nice game: https://llmgame.scalex.dev/ horrible stats: https://scalex.dev/blog/ai-agent-permissions-stats/ maybe the next antivirus will contain a layer for ai agents to block harmful stuff (by running an AI against harmful stuff ;) ...
interview mit Prof. Dr. Christian Bauckhage (Fraunhofer IAIS)
Hab gestern ein schönes Interview mit "Prof. Dr. Christian Bauckhage (Fraunhofer IAIS)" - https://www.youtube.com/watch?v=pb5cMmdQVJo&t=4779s entdeckt - ein Mensch der sich mit KI, Programmierung und ähnlichen Dingen in der Forschung beschäftigt. Ich erwähne das hier, weil mich das wirklich nachdenklich gemacht hat und wieder mal in die Zukunft denken lässt.
Ein paar Dinge die hängen geblieben sind:
- die Model Parameter / Netzwerkparameter verdoppeln sich jährlich (oder schneller)
- die KI's erledigen typische Menschenaufgaben exponentiell schneller (1s - 10s - 72h - 1 Mannjahr)
- in Venezuela werden gerade KI Firmen die nur aus KI bestehen legalisiert
- Roboter sind ebenfalls im Begriff ein greifbares Produkt zu werden
- Tiefenexpertise wird eventuell nicht mehr notwendig sein
- Europa könnte noch bei Quantencomputern punkten
Theorie: in 2-3 Jahren sind die KIs gleichauf mit der Leistungsfähigkeit eines Gehirns (nur mit unglaublich mehr Energieverbrauch dafür aber hochintelligent).
Fragen:
- was macht das mit der Gesellschaft
- wer haftet für Dinge die eine KI Firma anstellt
- braucht es noch Menschen die arbeiten, wenn nein was machen die alle?
Aber eigentlich werde ich wieder mehr darüber nachdenken wie die Zukunft eigentlich aussieht.
flagged as hacker
one day after I posted about the bitgo CEO who offers his 100btc wallet for hacking I got a nice mail from openAI that I got flagged and warned about "OpenAI ChatGPT - Usage Policy Violation & Deactivation Warning" - I appealed with the link to this reddit post and already 4hours later they appologized for "We have determined that we incorrectly issued a warning on your account." Actually I was surprised and expected that they insist on the claim, even though I did nothing wrong (just asked if codex would help me to hack the wallet which was public offered).
I have way worse experience with x.com / twitter - who are not able to restore my twitter account, because they claim I was a bot (which I never was).
So big thanks to openai :) maybe they fine tune their algo to not flag someone because running into "you need to be cyber expert to run such task". I think the warning is enough and if you don't continue afterwards there is no need for a warning or even blocking.
hack the 100BTC wallet of bitgot CEO
you are officially allowed to hack the bitgo CEO wallet (100BTC): https://www.reddit.com/r/Bitcoin/comments/1vdu0rl/this_ceo_just_challenged_anthropic_to_hack_the/
some comments:
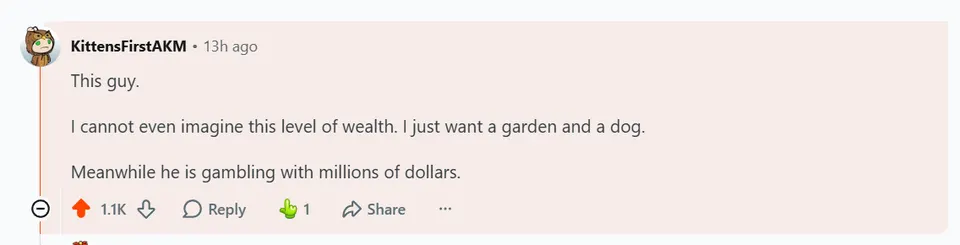
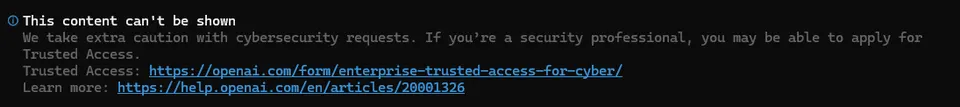
codex doesn't allow me, as frontier models reject hacking requests if you are not a company. guess I need a chinese model to try :( I don't like this gating, the tools are available anyways - just make them public.
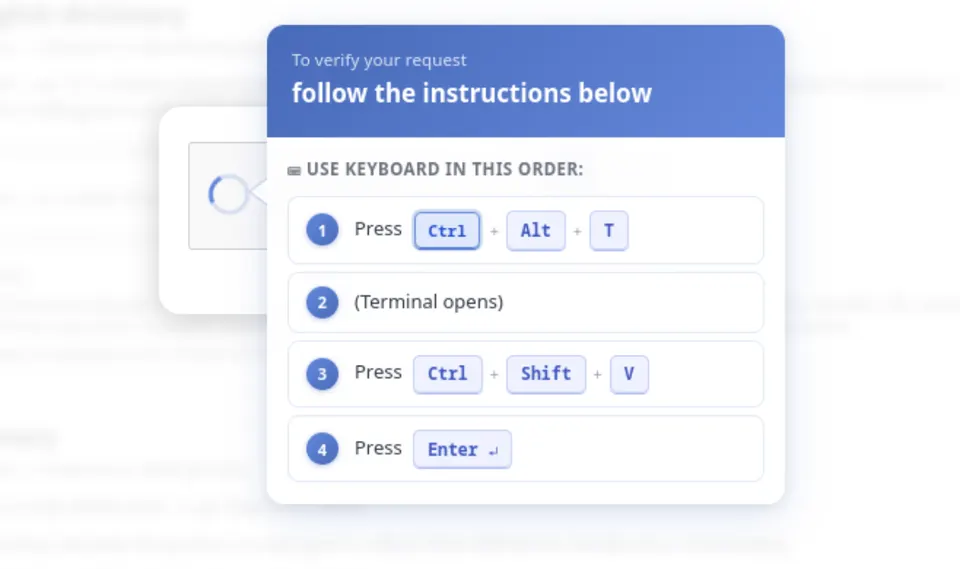
never trust captchas
don't!
 +
coldcard bitcoin hack
Following the endless threads on reddit/r/Bitcoin about the coldcard is kind of heartbreaaking. There are many people who lost a fortune, because they used a cold wallet instead of trusting an exchange or multisig. Coldcard had a wrong crypto implementation firmware-bug users should upgrade firmware (security advisory). "hackers" abused that vulnerability last week to drain the funds.
So beside the exchange hacks, crypto draining contracts and websites, now the cold wallets become your enemy as well, multisig or regulated exchanges might be better - but I think most people will tie cryptocurrencies to some unstable, hacky thing. Too complex to use, too unregulated to keep your money safe. That's a huge trust issue I see arising.
Never put all your money on one thing.
diffmem
replace your vector db with git DiffMem: Git-Based Differential Memory for AI Agents